Closing the books at EOFY usually means invoices, payroll, BAS prep, accountant questions, and a last push to tidy the numbers before 30 June. For most small business owners, cyber security drops down the list because it doesn’t feel urgent until something goes wrong. That’s exactly why this period is risky. Attackers know finance teams are busy, approvals get rushed, inboxes fill up with payment requests, and people are more likely to click first and check later.
An effective eofy cyber security checklist for australian small businesses needs to be practical, not theoretical. You don’t need a glossy policy folder that no one opens. You need a short, structured plan that tells you what to check, who owns it, and what has to be fixed before the new financial year starts. That means reviewing systems, locking down access, testing backups, tightening financial workflows, and making sure staff know what EOFY scams look like.
If you treat EOFY cyber work like a mini-project, it becomes manageable. Put dates against each task. Assign an owner. Decide what gets done this week, what gets done before 30 June, and what needs outside help.
EOFY is when businesses handle more sensitive financial information than usual. It’s the worst time to discover that an old account still has admin access or that backups haven’t been tested.
TLDR
The end of the financial year is a smart time to run a focused cyber security reset across your business. This eofy cyber security checklist for australian small businesses covers eight practical priorities, from auditing your systems and patching devices to enforcing MFA, testing backups, reviewing access, and improving staff awareness. Done properly, this helps protect financial data, supports compliance obligations such as the Notifiable Data Breaches scheme, and gives you a cleaner, safer start to the new financial year. The best approach is to treat it like a short project with clear owners, realistic deadlines, and outside support where needed.
1. Conduct a Comprehensive Cyber Risk Assessment and Audit
EOFY often exposes the same problem. A business owner asks for a quick security check, and we find three old staff accounts still active, a forgotten NAS in the comms cupboard, and a finance app connected to a personal email address. None of that looks dramatic on its own. Together, it creates easy ways into payroll data, client records, and email.
The first job is to map what your business uses. That means devices, user accounts, cloud apps, shared mailboxes, backup systems, remote access tools, Wi-Fi equipment, and any subscription that touches business data. If it can store data, move data, or log into something important, put it on the list.
The Australian Signals Directorate’s Annual Cyber Threat Report notes cybercrime is reported in Australia about every six minutes. EOFY is a risky time because teams are busy, approvals get rushed, and old access often stays in place longer than it should.
What to check first
Start with four areas:
- Assets: Laptops, phones, servers, firewalls, NAS devices, printers, and cloud platforms.
- Accounts: Staff, contractors, shared logins, admin accounts, and former users who may still have access.
- Data paths: Where financial files live, who can reach them, and which apps sync or export them.
- Ownership: Who approves access, who maintains the system, and who responds if something goes wrong.
This is also the right point to line your review up with the ACSC Essential 8 approach for small business. It gives you a practical baseline instead of a vague “check everything” exercise.
Common audit findings in small businesses
A proper review usually turns up familiar issues:
- Unknown devices: Old laptops or personal phones still connected to company email or file storage.
- Unused accounts: Former staff, bookkeepers, or vendors who still have logins.
- Unclear admin rights: Nobody can say who has admin access to Microsoft 365, payroll, backups, or the firewall.
- Shadow IT: Staff signing up for tools with a business email address and no security review.
- Weak records: No current list of systems, owners, or recovery steps.
EOFY Audit Mini-Project. Week 1
Treat this as a short project, not a one-off IT tidy-up.
| Task | Owner | Due Date | Status |
|---|---|---|---|
| Export user lists from Microsoft 365, finance apps, and key platforms | Office manager or IT provider | Day 1 | Not started |
| List all business devices and note who uses each one | Operations manager | Day 2 | Not started |
| Identify admin accounts and shared mailboxes | IT provider | Day 3 | Not started |
| Review former staff and contractor access | Business owner and HR/admin | Day 4 | Not started |
| Mark risks as Fix now, This month, or Monitor | Business owner and IT provider | Day 5 | Not started |
That table sounds simple because it should be. Small businesses do better with a short list, named owners, and a deadline that fits into a real week.
Turn findings into actions
An audit only helps if it produces decisions. For each item you find, record four things: what the risk is, who owns it, what action is required, and when it will be closed. I usually sort them into three buckets: fix now, fix this month, and accept with monitoring. That keeps the list usable and stops lower-value issues clogging up urgent work.
Use a practical rule. If you cannot say who owns a system, who has access to it, and how its data is protected, treat it as an open risk.
A shared finance mailbox is a good example. If invoice approvals, remittance advice, and payroll notifications all flow through one mailbox and nobody has reviewed access in two years, the problem is already there. EOFY is the right time to clean it up, assign ownership, and document the result.
2. Update and Patch All Systems and Software
A lot of EOFY clean-up feels administrative. Patching is different. It closes known holes that attackers already know how to use.
The pattern is familiar. A business updates laptops but forgets the firewall. Or Microsoft 365 stays current while the PDF tool, browser extension, NAS, or reception PC falls behind. One missed system is often enough.
At EOFY, that risk goes up because staff are in finance systems more often, invoice traffic increases, and people are working faster than usual. According to verified EOFY guidance for Australian SMEs, 82% of Australian small businesses experienced a cyber incident in 2024. Unpatched software and weak MFA were listed among the common issues.
What to patch first
Start with the systems that would cause the most disruption if they were compromised or unavailable. In small business environments, that usually means endpoints first, then business apps, then network gear, then the odd legacy system everyone is afraid to touch.
Use this order:
- Operating systems: Confirm Windows, macOS, iOS, and Android updates are turned on and installing successfully.
- Core business apps: Update Microsoft 365 apps, browsers, PDF software, antivirus, finance tools, and any plugins tied to payroll or invoicing.
- Infrastructure: Check firewall, router, Wi-Fi access points, switches, NAS devices, and remote access tools for firmware updates.
- Older systems: Identify devices or software that cannot be patched. Record them and limit what they can reach on the network.
That last point matters. If an old workstation runs a line-of-business app that breaks on newer versions, the answer is not to ignore it for another year. Isolate it, restrict internet access, and put a replacement date against it. That is a business decision, not just an IT one.
What works in practice
Automatic updates handle a lot of the heavy lifting, but only if someone checks that they are succeeding. I see small businesses assume patching is covered because the setting is enabled. Then we log in and find failed updates, postponed restarts, or a firewall that has not had firmware attention in 18 months.
Assign patching to a named owner. If you have an internal admin person, they can track status while your IT provider handles the technical work. If you want a repeatable method for rolling out security controls across staff devices and cloud systems, a practical MFA rollout plan for business also shows the kind of ownership, sequencing, and communication that patching projects need.
Avoid the usual trap of asking staff to update devices when they have time. Reception, sales, and accounts teams will always have a reason to defer a restart, especially in June. Set a maintenance window, communicate it clearly, and follow up on the machines that miss it.
A simple EOFY patch schedule
For most small businesses, a simple rhythm works better than an ambitious one that nobody keeps.
- Weekly: Endpoints, browsers, Microsoft 365 apps, antivirus, mobile devices.
- Monthly: Firewalls, network gear, NAS devices, printers, specialty business software.
- Same day for critical fixes: Apply urgent security patches as soon as they are tested and approved.
One stubborn device can become the weak link. The front desk PC that never restarts is a classic example. Schedule it after hours, confirm the updates installed, and move on.
If patching is manual in your business today, EOFY is the right time to turn it into a small project with an owner, a schedule, and a checklist. That is how this stops being a recurring problem.
3. Implement or Strengthen Multi-Factor Authentication MFA
A common EOFY fraud scenario starts with one stolen mailbox password. From there, an attacker can read invoice threads, reset other logins, and send payment-change emails that look legitimate. MFA cuts off a large part of that risk by requiring a second proof of identity before access is granted. The Australian Cyber Security Centre recommends MFA as one of the most effective baseline controls for small businesses, and it aligns directly with the Essential Eight.
That matters because MFA is not just an IT setting. It is a short, contained project with a clear outcome. By the end of the rollout, every high-risk account should be protected, exceptions should be documented, and staff should know how to sign in without calling the office manager in a panic.
Where MFA matters most
Start with accounts that give an attacker reach, money, or control. Email is first. If someone gets into a mailbox, they can monitor conversations undetected for days before anyone notices.
Next, cover:
- Cloud platforms: Microsoft 365, Google Workspace, SharePoint, OneDrive
- Finance systems: Xero, MYOB, payroll, expense tools, payment gateways
- Remote access: VPN, remote desktop gateways, remote support tools
- Privileged accounts: Global admins, local admins, backup admins, security admins
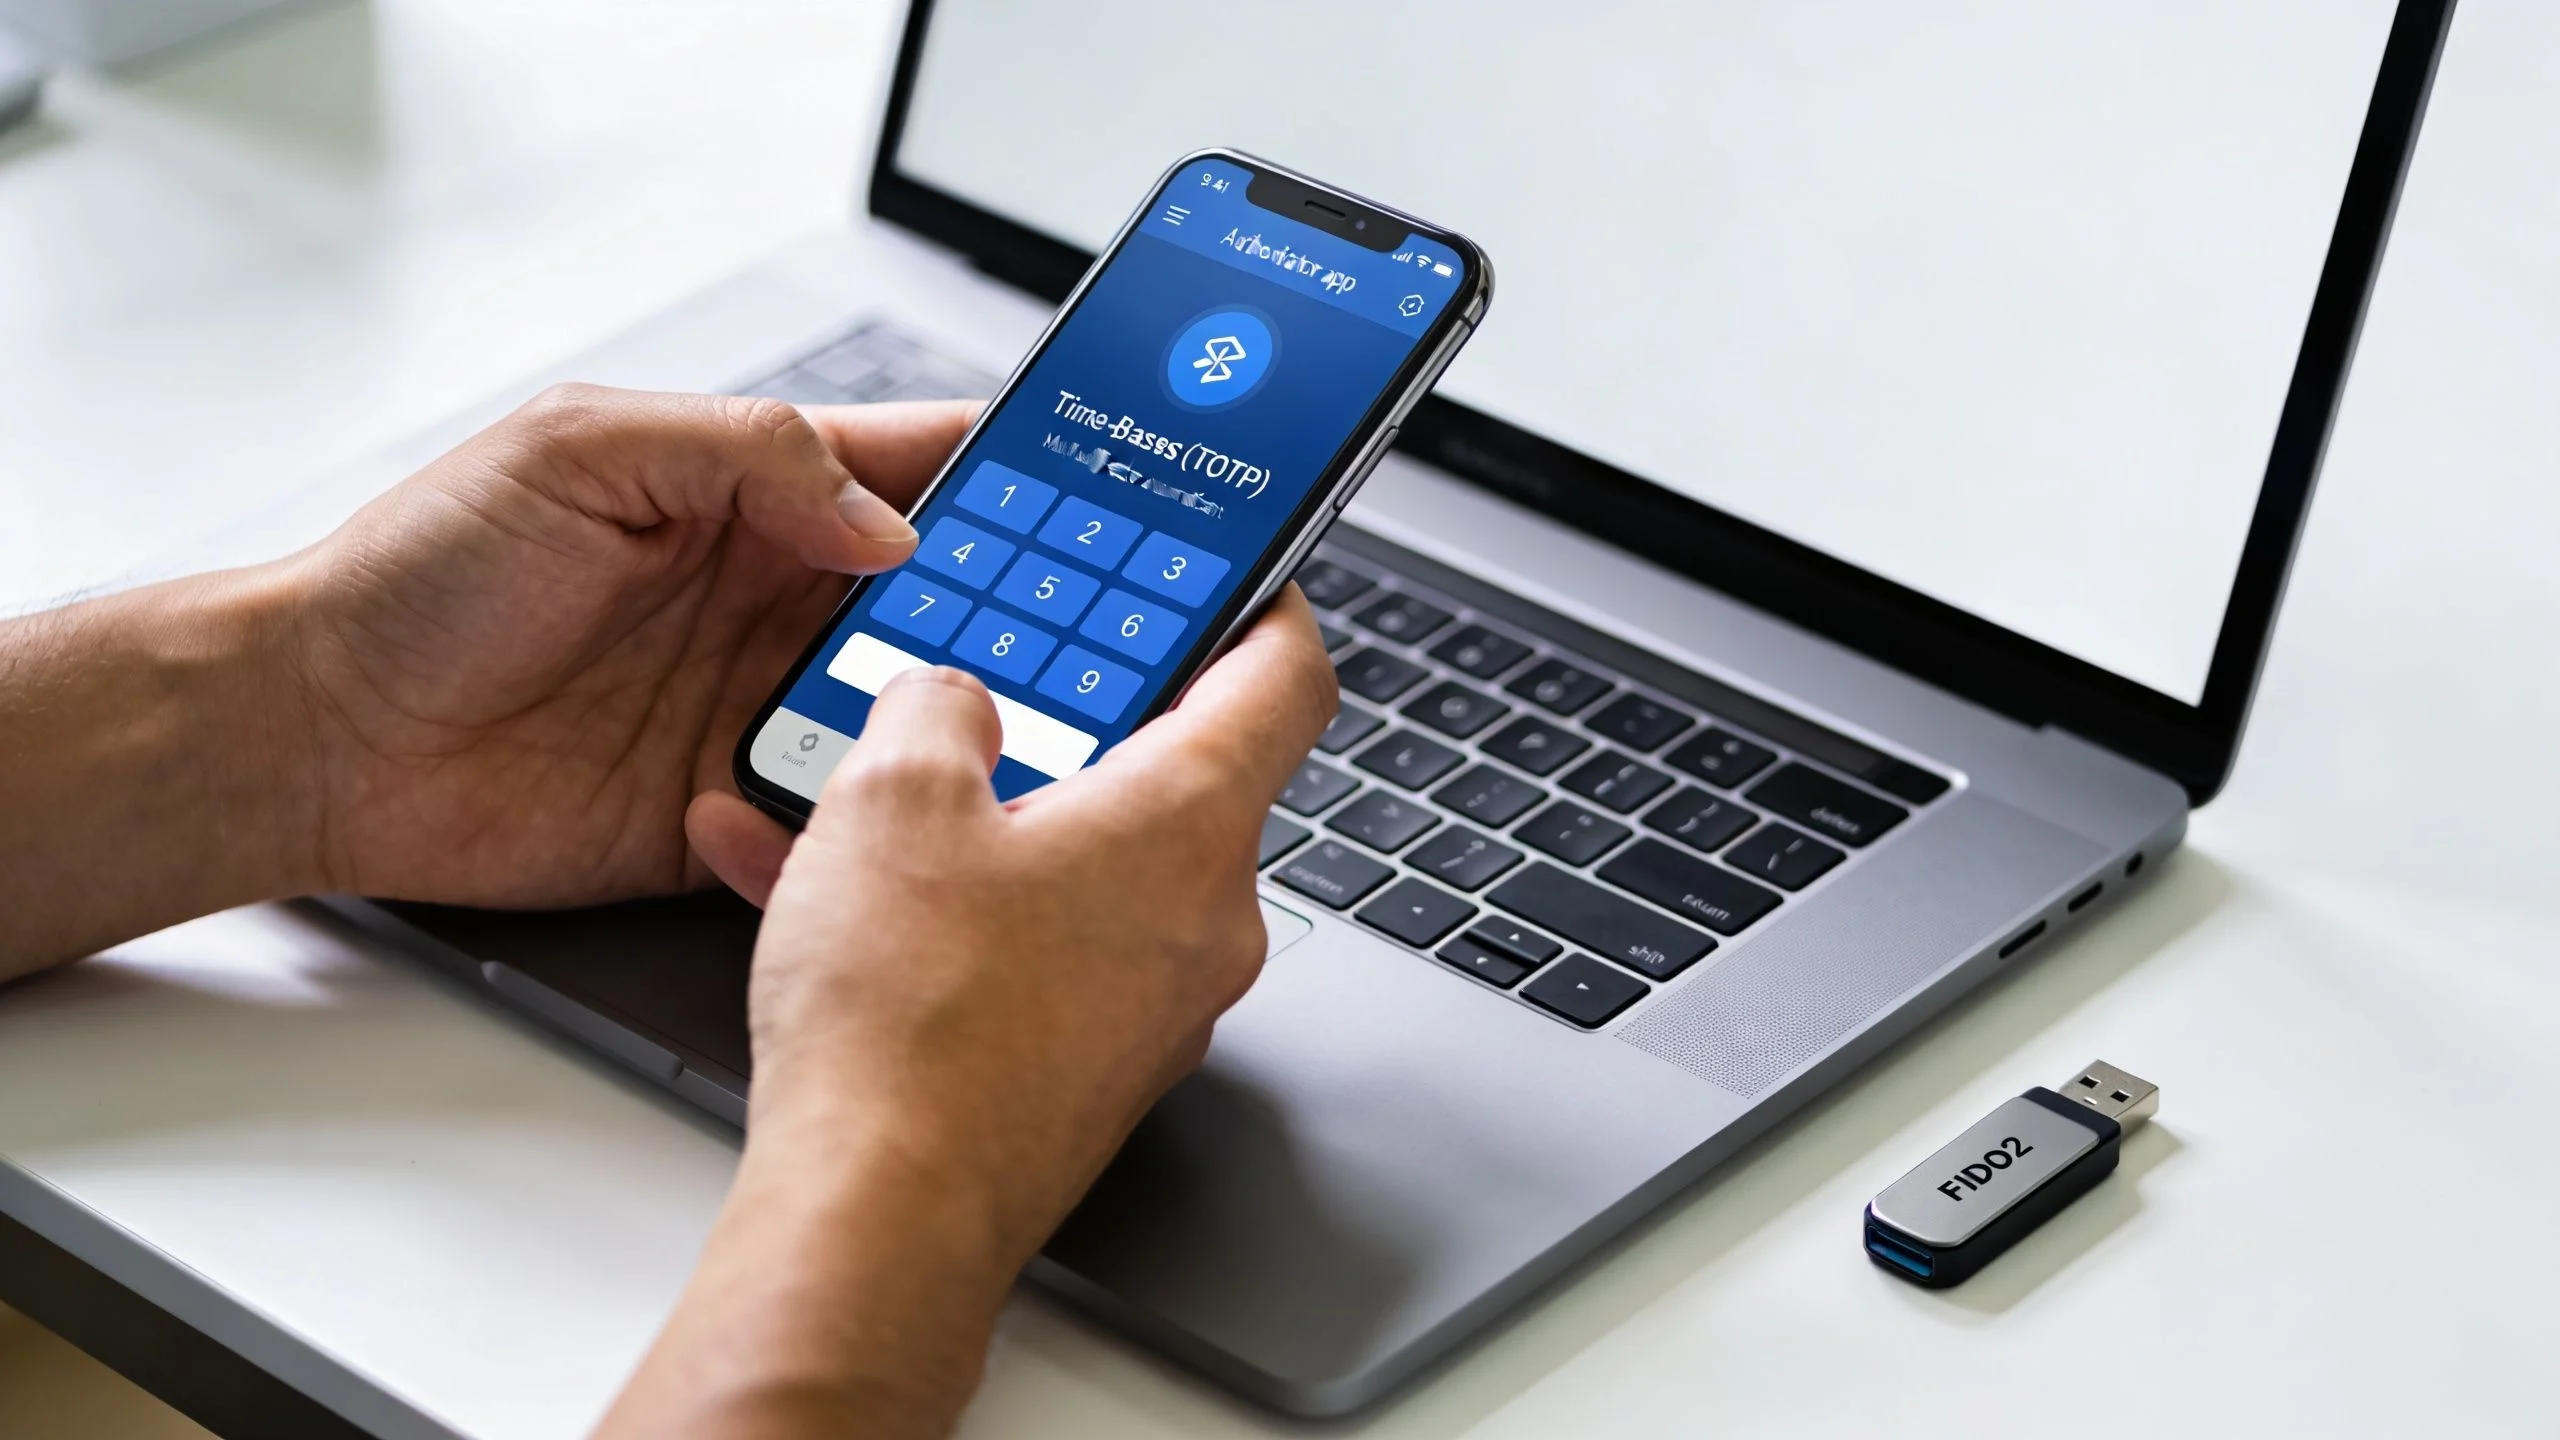
Use stronger methods where possible. Authenticator apps are a good baseline. FIDO2 security keys are better again for admin accounts and finance approvers. SMS codes still have value if that is the only option a legacy system supports, but they should not be the first choice for critical access.
If you need a practical rollout sequence with owners, stages, exclusions, and staff communication, this MFA rollout plan for business is the right kind of model.
Run MFA as a small EOFY project
The businesses that do this well keep it simple.
Set an owner. Define the systems in scope. Pick an enrolment window. Test with a small group first, usually directors, finance, and internal admins. Then enforce MFA in stages across the rest of the business.
That staged approach matters because older apps, shared devices, and service accounts often break first. It is better to find that on a Tuesday afternoon than during payroll or supplier payment runs. I also recommend documenting two things before enforcement begins: who can approve temporary exceptions, and how locked-out users will be verified and assisted.
Mistakes that create gaps
Partial rollout is the big one. If MFA is enabled for half the team, attackers will target the other half.
The next issue is forgetting non-human or edge-case access. Shared mailboxes, break-glass admin accounts, backup consoles, scanner-to-email accounts, and remote support tools are easy to miss. Each one needs a decision: protect it with MFA, replace it, restrict it, or retire it.
Another common mistake is treating enrolment as a technical task instead of a change process. Staff need clear instructions, a deadline, and a support contact. A one-page setup guide usually prevents a lot of confusion.
If an account takeover still occurs, MFA will limit the blast radius, but you still need actionable incident recovery steps ready so the business can respond quickly.
A good EOFY outcome is straightforward. High-risk systems have MFA enforced, stronger methods are used for sensitive roles, exceptions are written down, and someone owns the follow-up for the accounts that missed the first pass.
4. Review and Update Access Control Policies
Access sprawl is one of the most common problems I see in small businesses. Someone starts in admin, helps with payroll for six months, then moves roles but keeps the same permissions. A contractor finishes a project but their login remains active. An old shared mailbox still has forwarding enabled to a private account. None of this feels urgent until there’s an incident.
EOFY is a good trigger for a permissions clean-up because teams are already reviewing responsibilities and financial workflows. The principle of least privilege is especially important. Give people the access they need to do their job, not the access that’s easiest to leave in place.
The review most businesses need
Run an access review against your key systems. Check email admin roles, accounting software access, bank file preparation workflows, HR files, backups, and shared drives that hold contracts or employee data.
Use a simple owner-based model:
- Business owner or director: Approves high-risk finance and admin access.
- Manager: Confirms role-based access for their team.
- IT or MSP: Implements changes, disables old accounts, documents admin rights.
This is also the right moment to remove accounts for former staff and expired contractors. Don’t just disable sign-in if the data still matters. Review mailbox delegation, file ownership, forwarding rules, and mobile device sign-ins as well.
Focus on high-consequence access
Not all permissions carry the same risk. If a staff member has read-only access to a shared folder, that’s different from having authority to approve invoices, export payroll data, or grant admin rights in Microsoft 365.
A practical example is a bookkeeper who still has broad admin access to multiple platforms after changing scope. If their account is compromised during EOFY, the attacker may not need to break in anywhere else. The account already opens the door.
A good access policy should answer one simple question for every account. What business reason justifies this level of access right now?
5. Test Backups and Update Your Incident Response Plan
EOFY is a common time for one bad click to turn into a business interruption. An accounts mailbox gets phished, files start disappearing, and the first question is no longer whether backups exist. It is whether you can restore the right data fast enough to keep trading.
The 3-2-1 backup rule is still a sound baseline for small businesses: keep three copies of data, store them on two different media types, and keep one copy offline or off-site. It helps cover the failures I see most often in smaller environments: accidental deletion, device failure, sync issues, and ransomware reaching more than one system.
Test restores against business priorities
A backup dashboard can say everything completed successfully and still leave you stuck during an incident. The ultimate test is simple. Can you restore the files, mailboxes, or systems your business depends on, and can you do it within a timeframe the business can tolerate?
Start with the items that would stop cash flow, service delivery, or compliance work:
- Finance data: Xero exports, payroll records, invoices, BAS documentation
- Operational files: shared drive folders, contracts, customer records
- Identity systems: Microsoft 365 data, admin configurations, key mailboxes
- Local systems: servers, NAS devices, line-of-business applications
Treat this like a short EOFY project, not a vague IT task. Assign an owner, set a date, test one restore from each category, and record how long it took, what failed, and what still relies on one person knowing where everything lives.
If you need a starting point, these disaster recovery plan examples for Australian businesses help turn backup testing into a documented process, and these actionable incident recovery steps are useful for mapping the first few hours after an incident.
Write the incident plan for a bad day
A good incident response plan works when people are under pressure, short on facts, and making decisions quickly. Keep it short enough to use. Name who declares an incident, who contacts IT or your MSP, who approves taking a system offline, who handles customer communication, and how finance approvals are paused if email or accounting systems are affected.
Be specific about the first hour. Which accounts get disabled first? Which devices are isolated? Where are clean backups stored? Who can authorise external help? If your plan lives in one person’s inbox, it is not much of a plan.
A practical EOFY exercise is to run one tabletop scenario with your leadership team. For example, a staff member opens a fake invoice, enters Microsoft 365 credentials, and the mailbox starts sending phishing emails internally. Walk through the first 60 minutes, note the gaps, then update the document straight away. That is the difference between a checklist item and a response plan your business can use.
When to get help
EOFY work can look manageable until you realise half the job depends on knowledge that sits with one person, one inbox, or one ageing laptop. That is the point to bring in outside help.
Get support if you cannot answer basic operating questions quickly. Which devices still connect to company systems? Who approves changes to Microsoft 365, Xero, banking access, or backup settings? Which admin accounts are shared? If those answers are unclear, treat EOFY cybersecurity as a short project, not a loose collection of tasks.
A good provider should give you a defined scope, owners, and dates. Ask for a time-boxed review that covers your current risks, the fixes that can be completed before 30 June, and the work that should roll into next quarter. That approach keeps costs under control and stops the review from turning into a vague “security clean-up” that never finishes.
If budgeting is part of the delay, use this IT budget planning guide for Australian small businesses to separate urgent remediation from longer-term improvements.
This is also the right time to get outside advice if your business handles payroll, customer identity documents, or supplier banking changes. Those areas carry direct fraud risk, and the practical controls often overlap with the Australian identity theft prevention tips finance teams already need.
Tbourke Solutions can assist with that kind of focused review, particularly where EOFY priorities need to line up with day-to-day operations and the Essential Eight.
6. Conduct Cybersecurity Awareness Training and Phishing Simulations
Friday afternoon. Payroll is due, invoices are stacked up, and someone in accounts gets an email that looks like a supplier asking for new bank details before the payment run closes. That is how EOFY fraud usually starts. Not with a complex breach, but with a rushed decision by a busy employee.
Training at this time of year needs to match that reality. Generic annual modules do little if they never cover fake ATO notices, invoice redirection, business email compromise, or urgent approval requests sent from a phone-friendly email.
Train for the scams your team will actually see
Keep it short and specific. A five-minute refresher on one scam pattern will usually stick better than a 45-minute presentation staff forget by lunch.
Show your team examples they are likely to face during EOFY:
- Fake invoice emails: Slightly altered sender domains, changed bank details, or urgent payment language
- ATO or myGov lookalikes: Links to credential-harvesting pages dressed up as tax or compliance notices
- Supplier impersonation: Requests to update payment details or resend remittance advice
- Executive-style pressure emails: Messages that push staff to act outside normal approval steps
- Malicious attachments and QR codes: Files or codes that bypass a quick visual check
Different roles need different examples. Finance staff should practise verifying payment changes. Operations staff should know how to treat delivery notices and shared file links. Field staff using phones need to spot the red flags that are easy to miss on a small screen.
A practical format looks like this:
- Five-minute refreshers: One topic each week during EOFY
- Role-based scenarios: Finance, admin, warehouse, and remote staff each get relevant examples
- A clear reporting path: One mailbox, one button, or one Teams channel for suspicious messages
- Phishing simulations: Safe internal tests that measure whether people stop, check, and report
Businesses that want a repeatable staff program can use security awareness and training for staff.
Good training teaches staff when to pause, verify, and escalate.
Make reporting easy and useful
If reporting feels clunky, staff will delete the email and move on. Keep the process simple. One action, one destination, fast feedback.
Then close the loop. If a staff member reports a suspicious message, acknowledge it and explain what it was. That is how people build judgement. A simulation also needs follow-up. The point is not to catch people out. The point is to show where habits break down before a real attacker finds the same gap.
Treat this like a small EOFY project, not a one-off training task. Assign an owner, set a two to four week schedule, choose the scenarios to test, and record who needs extra coaching. That structure fits the Essential Eight focus on user application hardening and reducing the chance that a single click turns into a business problem.
7. Secure Financial Data and Review Vendor Security
At EOFY, finance teams move faster than usual. Payroll is being finalised, BAS and tax documents are being shared, suppliers are sending invoices, and staff are updating records under time pressure. That combination creates a narrow, busy corridor for sensitive data. If an attacker wants to redirect a payment or harvest identity information, this is one of the best times to try.
Email often sits in the middle of that corridor. Invoice approvals, bank detail changes, remittance advice, and payroll queries usually pass through a mailbox before they reach your accounting system. A secure file in the right folder does not help much if the approval step happens in an exposed inbox.
Lock down the finance path
Financial data moves like a handoff chain. One weak handoff is enough.
Start with the systems and accounts that touch money or personal information, then work outward through the process. For a small business, that usually means reviewing:
- Accounting platforms: Confirm MFA is enabled, admin access is limited, connected apps are still needed, and audit logs are turned on.
- Invoice and payment workflows: Require a second check for supplier bank detail changes and any urgent payment request.
- Shared mailboxes: Review who can access accounts@, payroll@, and admin@. Remove old permissions and forwarding rules.
- Stored financial files: Check where payroll exports, tax records, and customer payment data are saved. Limit access to the staff who need it.
- Email protections: Verify SPF, DKIM, and DMARC are set correctly for the domains used in finance communications.
A simple rule works well here. No payment detail change gets actioned from email alone. Staff should verify it through a known phone number, an existing contact, or a second approver inside the business.
If you are reviewing exposure around employee records, customer details, and fraud risk at the same time, these Australian identity theft prevention tips are a useful companion read.
Review vendors like part of your own environment
Small businesses often hand payroll, bookkeeping, payment processing, document storage, and software administration to outside providers. That saves time, but it also extends your risk boundary. If a vendor has access to your data or your systems, their security controls affect your business directly.
You do not need a long procurement process. You do need a short, repeatable vendor review. Ask practical questions:
- Who on the vendor side can access your data?
- Do they use MFA for staff and contractors?
- How do they separate your data from other clients?
- How quickly will they tell you about a breach or suspicious access event?
- What logs can they provide if you need to investigate a payment issue or account takeover?
- When did they last review access for former staff?
A payroll provider is a good example. They may hold employee identities, bank details, tax file numbers, and super information in one place. If their support account is poorly protected, your own internal controls may not stop the fallout.
Treat this as a small EOFY project. Assign one owner, list your finance-critical vendors, send a standard question set, and record the answers in one place. That gives you something more useful than a checklist tick. It gives you a clear list of gaps, owners, and follow-up actions that fit into your July security plan and align with the Essential Eight focus on restricting access and reducing the impact of account compromise.
8. Establish Your Cybersecurity Budget for the New Financial Year
July budgets often get locked in after decisions on staff, stock, software renewals, and equipment. If cyber security is left until the end, the business usually funds whatever feels urgent, not what reduces risk fastest.
Treat EOFY budgeting as a short project, not a shopping exercise. Start with the gaps already identified in your audit and assign each one an owner, an estimated cost, and a target quarter. That gives you a practical plan for the next 6 to 12 months, not a wish list that gets ignored by August.
Fund the controls that match your actual gaps
Good security budgeting is boring in the right way. It pays for the controls your team will maintain, review, and use properly.
Typical line items include:
- Identity and access: MFA, password management, privileged access controls
- Endpoint and system hygiene: endpoint protection, patch management, device monitoring
- Recovery capability: backup improvements, restore testing, disaster recovery documentation
- People and process: staff training, phishing simulations, policy updates
- Specialist support: MSP help, external reviews, incident response retainer hours
For many small businesses, the trade-off is not whether to spend money. It is where to spend first. A business with weak backup testing should usually fix that before buying another dashboard. A team still sharing admin accounts should sort identity controls before paying for advanced detection tools. The Australian Essential Eight is useful here because it helps separate baseline controls from nice-to-have extras.
Build the budget in phases
The strongest budgets are staged.
Split your plan into three buckets: immediate fixes for the next 30 days, core improvements for the next quarter, and deferred items for later in the financial year. That approach helps cash flow, reduces change fatigue, and makes progress easier to track. It also gives business owners a clearer way to approve spending because each item is tied to a risk, a deadline, and a person responsible.
If you need a framework for that process, this IT budget planning guide for small business is a useful reference for linking cyber spend to wider operating priorities.
Budget for upkeep as well as purchase costs. A tool that no one reviews, tunes, or renews is like installing a new alarm and never checking whether the batteries still work.
EOFY Cybersecurity: 8-Point Comparison for Australian Small Businesses
| Initiative | Implementation Complexity 🔄 | Resource Requirements ⚡ | Expected Outcomes 📊⭐ | Ideal Use Cases 💡 | Key Advantages ⭐ |
|---|---|---|---|---|---|
| 1. Conduct a Comprehensive Cyber Risk Assessment and Audit | 🔄 Moderate–High: organisation-wide discovery and analysis | ⚡ Time, asset inventory tools, scanners, possible external assessor | 📊 Comprehensive asset inventory, vulnerability list, risk-prioritised roadmap; ⭐ High for informed decisions | 💡 Starting point for EOFY security planning and budget justification | ⭐ Holistic visibility; enables targeted remediation and compliance mapping |
| 2. Update and Patch All Systems and Software | 🔄 Low–Moderate: routine but requires coordination and testing | ⚡ Admin time, patch management tools, maintenance windows | 📊 Reduced exploitable vulnerabilities; ⭐ High immediate risk reduction | 💡 Regular maintenance windows; urgent pre-EOFY hardening | ⭐ Fast, cost-effective mitigation of known vulnerabilities |
| 3. Implement or Strengthen Multi-Factor Authentication (MFA) | 🔄 Low: straightforward configuration and rollout | ⚡ Licensing (sometimes), authenticators/keys, user onboarding time | 📊 Dramatic reduction in account compromise (>99%); ⭐ Very High | 💡 Protect email, admin, remote access, finance systems | ⭐ Strong, scalable protection for identity compromise |
| 4. Review and Update Access Control Policies | 🔄 Moderate: requires audits, role analysis and policy changes | ⚡ Identity management tools, admin time, RBAC implementation | 📊 Reduced privilege creep and insider risk; ⭐ High for limiting blast radius | 💡 After role changes, contractor turnover, or compliance reviews | ⭐ Minimises excessive access and enforces least-privilege |
| 5. Test Backups and Update Your Incident Response Plan | 🔄 Moderate–High: testing, tabletop exercises and documentation | ⚡ Backup storage, test environments, stakeholder time, possible external facilitation | 📊 Validated recovery capability and clear response playbooks; ⭐ High for resilience | 💡 Ransomware preparedness and disaster recovery validation | ⭐ Ensures recoverability and reduces downtime in incidents |
| 6. Conduct Cybersecurity Awareness Training and Phishing Simulations | 🔄 Low–Moderate: program setup and ongoing campaigns | ⚡ Training platform, simulated phishing tools, staff time | 📊 Measurable drop in risky behaviours (click rates); ⭐ Moderate–High for human risk | 💡 Organisations with notable phishing exposure or compliance needs | ⭐ Improves human defence and reporting culture |
| 7. Secure Financial Data and Review Vendor Security | 🔄 Moderate: vendor assessment plus technical controls | ⚡ DLP tools, vendor questionnaires, audit time, MFA on finance systems | 📊 Reduced supply‑chain and financial data exposure; ⭐ High for financial integrity | 💡 EOFY when financial data flows peak and vendor access matters | ⭐ Protects highest-value data and strengthens third‑party assurance |
| 8. Establish Your Cybersecurity Budget for the New Financial Year | 🔄 Low–Moderate: requires risk-to-cost mapping and stakeholder buy‑in | ⚡ Risk assessment outputs, finance collaboration, vendor quotes | 📊 Funded, risk‑based security roadmap and clearer prioritisation; ⭐ Moderate–High | 💡 Annual planning cycle and post‑audit prioritisation | ⭐ Aligns spending to risk and simplifies stakeholder approval |
Turn Your EOFY Checklist into Lasting Cyber Resilience
A strong EOFY review isn’t about squeezing in one more admin task before 30 June. It’s about resetting your business so the next financial year starts with fewer weak points, clearer ownership, and better recovery options if something goes wrong. That’s the key value of an eofy cyber security checklist for australian small businesses. It turns a stressful period into a practical checkpoint.
The businesses that handle EOFY cyber work well usually do a few things differently. They keep the plan short. They assign owners. They focus on the systems that matter most, especially email, finance tools, user access, and backups. They also accept the trade-off that good security sometimes adds a bit of friction. MFA takes an extra step. Access reviews take time. Verifying bank detail changes slows a payment run. Those are worthwhile delays compared with the disruption of a compromised mailbox or a payment diversion scam.
What doesn’t work is treating cyber security like a once-a-year clean-up. Patching can’t happen only in June. Backup testing can’t happen only after a scare. Staff awareness can’t be a single slideshow that everyone forgets by the following month. EOFY is the trigger, but the habits need to continue.
If you’re a small business owner, school administrator, sole trader, or office manager, keep the mindset simple. First, know what you have. Second, reduce avoidable risk. Third, make recovery easier. That approach aligns well with the Essential Eight and with the practical realities of small business operations in Australia.
For businesses that want outside support, Tbourke Solutions is a local MSP based in Hillside, Melbourne, providing IT support, cybersecurity services, cloud solutions, consultancy, and security awareness training for small to medium businesses and related organisations. That kind of support can help if you need a structured EOFY review, help implementing controls, or ongoing IT management rather than a one-off fix.
The important part is to act before the rush gets worse. EOFY pressure creates exactly the kind of environment attackers look for. A calm, project-based review now is far easier than untangling a breach while trying to close the books.
Frequently asked questions
What key items should be on an EOFY cyber security checklist for a small business?
Cover the work in a clear order. Start by identifying your key systems, accounts, devices, and data. Then patch systems, enforce MFA, review who has access, test backup restores, confirm your incident response steps, check staff awareness, review finance and supplier risk, and set a cyber budget for the new financial year.
Treat it like a short EOFY project, not a loose to-do list. Give each task an owner, a due date, and a simple result such as “MFA enabled for all email accounts” or “restore test completed for Xero exports and file server data.”
Why is EOFY a higher-risk time for cyber attacks?
Because normal checks get rushed. Finance teams are processing more invoices, managers are approving payments faster, and staff are dealing with accountants, payroll, tax records, and supplier emails all at once.
That creates good conditions for phishing, invoice tampering, and mailbox compromise. Attackers do not need a complex breach if they can slip a fake payment request into a busy week.
Is MFA really necessary for a small business?
Yes. MFA should already be in place for email, Microsoft 365 or Google Workspace, finance systems, remote access, and any admin account.
A password on its own is like a front door with one lock that half the office reuses elsewhere. MFA adds a second check, which blocks a large share of the account takeover problems small businesses deal with.
How often should backups be tested?
Test them often enough that you trust the restore, not just the backup report. A green tick in a dashboard does not prove your files, systems, or cloud data will come back cleanly.
EOFY is a good point to run a restore test for your most important business data. For many small businesses, that means finance records, shared files, line-of-business apps, and key Microsoft 365 or Google Workspace data.
What if we already have antivirus?
Keep it, but do not assume it covers the rest. Antivirus helps detect known threats and some suspicious behaviour. It does not fix unpatched software, weak login security, poor access control, or untested backups.
Most incidents come from several small gaps lining up. One missed patch, one reused password, and one staff member approving the wrong prompt can be enough.
Do we need an incident response plan if we’re a very small team?
Yes. Small teams usually need a simpler plan, not no plan.
Write down who makes decisions, who contacts your IT provider, which systems get isolated first, how staff should report suspicious activity, and how you will keep trading if email or shared files go down. In a real incident, that short document saves time and reduces bad decisions.
When should we get outside help?
Bring in outside help if you cannot clearly answer basic questions about your environment. Examples include not knowing which accounts have admin rights, whether MFA is fully rolled out, whether backups can be restored, or which devices still miss patches.
That is usually the point where an internal checklist stops being enough. A good provider can turn the EOFY review into a scoped project with priorities, owners, and realistic timelines, instead of leaving you with a long list that never gets finished.
Share This Story, Choose Your Platform!