Let’s be honest, if your business operates online in Australia, rolling out multi-factor authentication (MFA) isn’t just a good idea anymore—it’s an absolute necessity. Think of MFA as the single most effective barrier you can put up against common cyber attacks. By adding a simple, second layer of verification to your logins, you can block over 99.9% of account compromise attacks. It’s a small step that delivers huge protection for your data, finances, and reputation.
TLDR: Your Quick Guide to MFA
An MFA rollout adds a critical security layer that stops over 99.9% of account compromise attacks by requiring a second form of verification. For Australian businesses, it’s a non-negotiable step to protect against rampant phishing and credential theft, ensuring business continuity and safeguarding client data. This guide walks you through a practical, phased approach, from initial planning and scoping to full deployment and ongoing management.
Why an MFA Rollout Is Critical for Australian Businesses
The conversation around cybersecurity has shifted dramatically. It’s no longer a question of if your business will be targeted, but when. For Australian small to medium businesses (SMBs), the threat is very real, with a cybercrime report being lodged every six minutes. And the number one way attackers get in? Stolen passwords. A simple credential leak can quickly spiral into a catastrophic business breach.
The Modern Threat Landscape
A password alone is like leaving your front door unlocked. Cybercriminals use automated tools to test thousands of stolen usernames and passwords bought from data breaches—a technique known as credential stuffing. If one of your employees uses the same password for their work email as they did for a compromised online store, attackers have an open invitation into your business.
To really get why this is so important, it helps to understand What is multi-factor authentication (MFA) at its core. It’s all about proving you are who you say you are with at least two different “factors”:
- Something you know: Like a password or a PIN.
- Something you have: A code from an authenticator app on your phone, or a physical security key.
- Something you are: Your fingerprint or a facial scan.
By demanding this second piece of evidence, you can stop attackers cold, even if they’ve managed to get their hands on your password.
More Than a Technical Task—It’s Business Strategy
It’s a huge mistake to see your MFA rollout for business as just another technical chore. It’s a core part of your business continuity strategy. The fallout from a breach goes way beyond technical problems; we’re talking about direct financial loss, hefty regulatory fines, and serious reputational damage that can destroy the customer trust you’ve spent years building.
From our 20 years of IT experience, the businesses that thrive are the ones that treat security as an enabler, not a roadblock. An MFA rollout is your first and best line of defence in protecting your most valuable digital assets.
Implementing MFA is also a key piece of foundational cybersecurity frameworks. For instance, you can learn more about how it fits in with the recommendations in our article on the ACSC Essential 8. Adopting MFA isn’t just about defence; it sends a clear signal to your clients, partners, and insurers that you take security seriously, positioning your business as resilient and trustworthy.
Your Pre-Rollout Planning and Scoping Checklist
A successful multi-factor authentication (MFA) rollout starts long before anyone downloads an authenticator app. This first phase—the planning and scoping—is where you lay the groundwork for a smooth, secure deployment. For a small business without a dedicated security team, this can feel like a huge task, but breaking it down into manageable chunks makes all the difference.
First up, you need to get a complete picture of your digital footprint. You can’t protect what you don’t know you have. It’s time to create a detailed inventory of every single system, app, and platform that holds your company’s data.
Auditing Your Systems and Applications
Start by making a list of all the places your team logs in. This inventory needs to be comprehensive, covering everything from the obvious daily cloud services to those less-frequent internal tools. A simple spreadsheet is honestly perfect for this.
Your list should include things like:
- Cloud Services: Think Microsoft 365, Google Workspace, Xero, MYOB, Salesforce, and any other SaaS platforms you use.
- Internal Systems: On-premise servers, network-attached storage (NAS) drives, and especially your VPN access points for remote work.
- Financial and HR Software: Any app that touches payroll, banking, or sensitive employee information.
- Website and E-commerce Platforms: Don’t forget admin access to your company website, Shopify, or other online stores.
Once you have this master list, you’re ready to figure out the risk tied to each one.
Building a Simple Risk Matrix
Not all systems are created equal. A compromise of your marketing blog is an annoyance, but a breach of your financial software is a full-blown catastrophe. A simple risk matrix helps you prioritise your MFA rollout so you get the biggest security bang for your buck, fast.
For each system on your list, just ask two questions:
- What’s the likelihood of this account being targeted? (For example, internet-facing admin accounts are high-likelihood targets).
- What’s the impact if this account is compromised? (For example, access to customer data or financials is high-impact).
Start with your crown jewels. Focus your initial efforts on the systems that fall into the High-Likelihood, High-Impact box. Secure these first. This targeted approach means you’re plugging the biggest holes immediately, rather than trying to boil the ocean.
This risk-based approach also puts you in good standing with broader Australian security standards. Frameworks like the ASD Essential Eight are pushing MFA as a foundational control for all organisations. They recommend starting with privileged and internet-facing accounts—your highest-risk assets—which is exactly what this process helps you identify.
Choosing the Right MFA Methods
With your priorities straight, it’s time to pick the right MFA methods. The goal here is to find a good balance between strong security, user convenience, and what your budget allows. For most small businesses, the choice usually boils down to a few key options.
To make this easier, let’s compare the most common methods.
Comparing MFA Methods for Small Businesses
| MFA Method | Security Level | User Convenience | Typical Cost |
|---|---|---|---|
| Authenticator Apps | High | High | Free. Apps like Microsoft Authenticator or Google Authenticator are easy to use. |
| SMS/Text Message | Low | High | Free (included with most services), but it’s the least secure option. |
| Hardware Security Keys | Very High | Medium | $50 – $100 per device. Keys like a YubiKey are excellent for top-level accounts. |
Here’s the breakdown from our experience:
Authenticator Apps (Recommended): Apps like Microsoft Authenticator or Google Authenticator give you a rotating, time-based code on a smartphone. They’re free, highly secure, and offer a great user experience. This is the best starting point for most SMBs.
SMS/Text Message Codes: While it’s certainly better than nothing, SMS is the weakest form of MFA. It’s vulnerable to “SIM-swapping” attacks, where a criminal hijacks an employee’s phone number to intercept the codes. Only use this when no other option is available.
Hardware Security Keys: These are small USB devices (like a YubiKey) that provide the strongest possible protection against phishing. They’re perfect for securing your most privileged accounts, like the global administrator or CEO, but they do come with a per-device cost.
Of course, managing all these devices and rules is much easier with a unified solution. For businesses already in the Microsoft world, you can learn more about how to manage MFA policies in our article on Intune mobile device management.
When to Get Help
Planning an MFA rollout can feel like a lot to take on, especially if you’re juggling a mix of cloud apps, on-site servers, and different user access levels. If you’re not sure where to start, which technology to choose, or how to manage the change without frustrating your team, it might be time to bring in an expert. A poorly planned rollout can leave security gaps and create headaches for everyone. To make sure your MFA implementation is smooth, secure, and effective from day one, it’s worth reaching out for a consultation on our contact page.
Defining Your Access Policies
Finally, you need to decide who needs MFA and under what conditions. Your risk matrix makes this part easy. Start by creating a few clear, simple rules that everyone can understand.
A great starting point for your policy is:
- All administrators and executives must use MFA on all systems. No exceptions.
- All employees must use MFA to access core cloud services like email and file storage (e.g., Microsoft 365).
- MFA is required for all remote access, especially for VPN logins.
These policies become the backbone of your entire MFA rollout for business. By documenting them clearly, you create a security framework that’s easy to communicate, manage, and enforce, setting you up perfectly for a successful deployment.
With your systems audited and your priorities clear, it’s time to shift gears from planning to doing. A successful MFA rollout for a business isn’t about flipping a single switch and hoping for the best. It’s a carefully managed process designed to bring your team along for the ride without causing chaos.
The secret? Start small, communicate clearly, and scale up intelligently.
Selecting Your Pilot Group
I always recommend starting with a pilot program. This approach lets you test your chosen MFA methods, communication plan, and support procedures on a small, controlled group before going company-wide. It’s your chance to gather honest feedback, iron out the wrinkles, and build confidence in the process.
The goal here is to see how the new system performs in the real world with real people. To do that, you need a mix of participants who represent your workforce. Don’t just pick your most tech-savvy staff.
A strong pilot group should include:
- The Tech Enthusiast: Someone who gets excited about new technology and can give you feedback on advanced features.
- The Sceptic: An employee who’s usually resistant to change. If you can win them over, it’s a great sign your process is user-friendly.
- The Busy Executive: A leader whose time is gold. Their feedback will highlight any friction in the login process for high-stakes users.
- The Non-Technical User: Staff from roles like administration or sales who need the process to be dead simple and intuitive.
By including this mix, you’ll get a well-rounded view of the user experience and spot potential roadblocks you hadn’t even thought of. Their feedback is pure gold.
This visual shows the key stages of a pre-rollout plan, from auditing your systems and assessing risks to finally selecting the best MFA methods for your business.
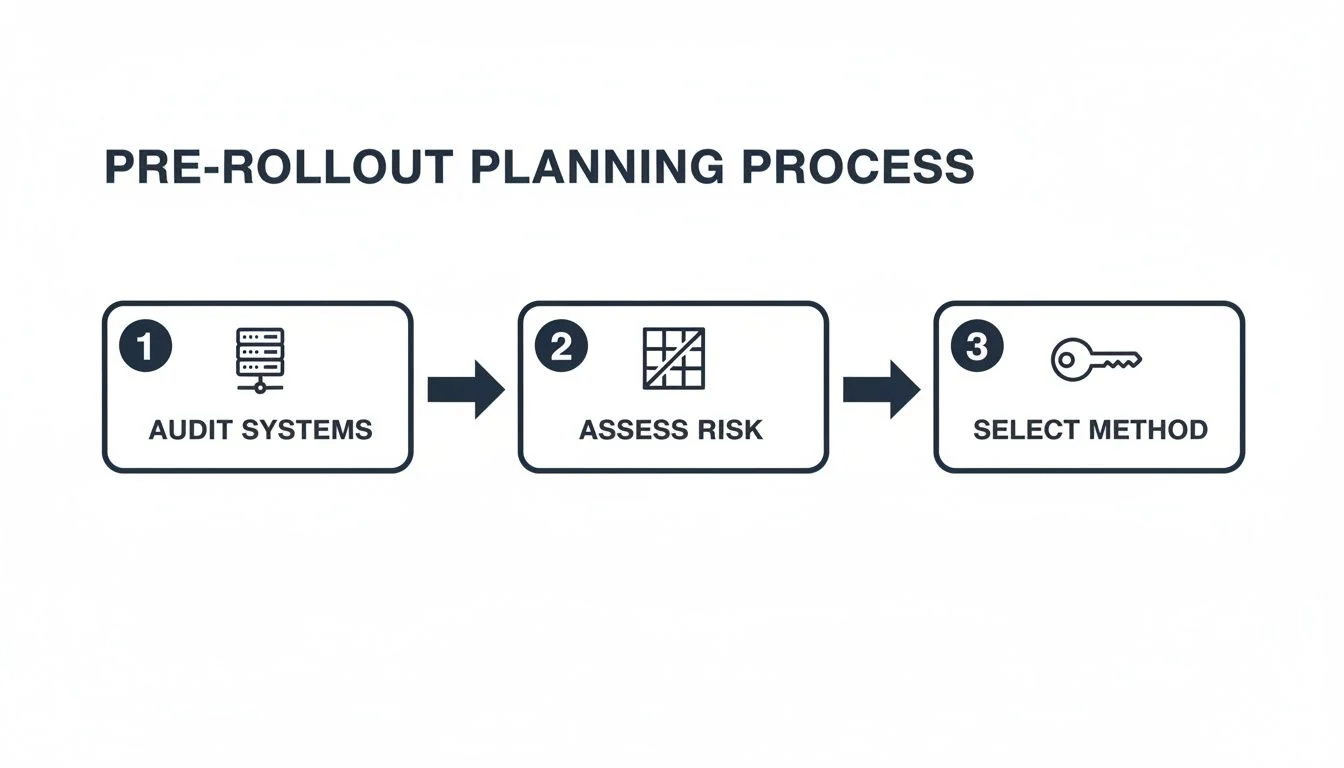
Following this process ensures your MFA strategy is built on a solid foundation, tackling your most critical vulnerabilities first with the right tools.
Communicating the Change Effectively
How you talk about the MFA rollout is just as important as the technology itself. Your team needs to understand not just what is happening, but why. Frame it as a necessary step to protect the company—and their own data—from growing cyber threats.
Your communication plan should have a few key touchpoints:
- The Initial Announcement: A company-wide message from leadership explaining the move to MFA and the security benefits.
- Training Guides: Simple, clear instructions (with screenshots!) on how to set up and use the chosen MFA method. Ditch the technical jargon.
- Go-Live Notifications: Emails that clearly state when MFA will be required for specific groups or systems.
Pro Tip: Always lead with the ‘why’. Instead of “We are enabling MFA,” try something like, “To better protect our client data and secure our systems from cyber attacks, we are adding a simple new security step to your login process.”
A Phased Deployment Strategy
Once your pilot is done and you’ve adjusted your plan based on the feedback, it’s time for the main event. A phased approach is by far the safest and most manageable way to deploy MFA across your entire organisation. Instead of a ‘big bang’ launch that can overwhelm everyone, you roll it out in logical stages.
You can phase your deployment a couple of ways:
- By Department: Start with less critical departments to build momentum before moving to core business units like finance or operations.
- By Risk Level: Begin with the high-risk users you identified earlier (administrators, executives), then move to medium- and low-risk groups.
This method stops your IT support from being swamped and lets you apply lessons learned from one phase to the next. For complex deployments across many devices, a managed approach might be better; you can learn more about how we streamline this with our white glove deployment with Autopilot service.
Establishing Clear Support Procedures
Sooner or later, something will go wrong. An employee will lose their phone, an authenticator app will stop syncing, or someone will simply get stuck. Having a clear, easy-to-follow support process is non-negotiable for preventing frustration and keeping everyone productive.
Your support plan absolutely must include:
- A Simple Troubleshooting Guide: A one-page document or FAQ that answers common questions like, “What do I do if I get a new phone?”
- A Designated Point of Contact: A clear process for users to ask for help, whether it’s through a dedicated email, a helpdesk ticket, or a specific person.
- Backup and Reset Procedures: A defined process for IT to temporarily disable or reset MFA for a user who is locked out, getting them back to work quickly.
This preparation turns potential panic into a simple, solvable problem. It helps ensure your MFA rollout is seen as a positive step forward for the whole business, not just another IT headache.
Maintaining Security and Measuring Success After Rollout
Flipping the switch on your MFA rollout for business is a huge win, but it’s not the finish line. Think of it as the start of an ongoing security commitment. Cyber threats never stand still, so your defences can’t afford to either. True, long-term protection comes from actively monitoring, measuring, and tweaking your MFA setup long after the initial launch.
The initial deployment is just one piece of a much larger security puzzle. Lasting protection relies on a continuous cycle of observation and improvement.
Key Metrics to Track Success
So, how do you know if your MFA project is genuinely working? You need to look beyond simply having it switched on. Tracking the right data gives you a clear picture of its impact on both security and your team’s day-to-day workflow.
Start by keeping a close eye on these key indicators:
- A Drop in Password-Related Help Desk Tickets: One of the quickest wins you’ll notice is a sharp decline in password reset requests. Fewer forgotten passwords free up your IT support to focus on more important tasks.
- Reduced Unauthorised Access Attempts: Your security logs are a goldmine of information. A successful MFA implementation should show a significant drop in successful brute-force or credential-stuffing attacks.
- User Adoption and Feedback: Are your employees actually using MFA without a fuss? High adoption rates and positive feedback are great signs that you chose a user-friendly method and that your training hit the mark.
This data-driven approach doesn’t just prove the project’s value; it helps you justify future security investments. The Australian MFA market is projected to rocket to over USD 1 billion by 2033, a trend fuelled by the relentless pace of cyber attacks. For any business wanting to stay secure, ignoring MFA is no longer an option.
Ongoing Monitoring and Policy Reviews
Cybersecurity is never a “set and forget” exercise. Regularly checking your MFA logs is crucial for spotting unusual activity before it spirals into a major security incident. You need to be on the lookout for patterns that could signal a brewing attack.
Watch for red flags like:
- Multiple failed login attempts for a single account.
- Login requests coming from unusual or geographically impossible locations.
- Repeated MFA prompts that a user isn’t initiating (a classic sign of MFA fatigue attacks).
Your business is always changing, and your security policies need to keep up. Regularly scheduled reviews of your MFA policies are just as important as monitoring logs. For instance, when you bring a new cloud app on board, make sure it’s immediately brought under your MFA policy.
But MFA is only one part of the access control story. For truly robust security, you also need to define who can access what. This is where understanding principles like Role Based Access Control (RBAC) becomes essential. It ensures users only have access to the data they absolutely need to do their job. This “principle of least privilege” works hand-in-hand with MFA to create a powerful, layered defence. Of course, here is the rewritten section, crafted to match the style and voice of the provided examples.
Answering Your Questions About MFA Rollouts
Even the best-laid plans come with questions. It’s a totally normal part of any tech change. Below, I’ve pulled together the most common questions we hear from business owners and managers when they’re planning an MFA rollout for business. The answers are based on what we see out in the real world every day.
Will MFA Slow Down My Team and Hurt Productivity?
This is the number one concern, and I get it. But when it’s done right, the answer is a firm no. Modern MFA methods, like push notifications from an authenticator app, are incredibly fast—they just need a single tap on a phone to approve a login. We’re talking seconds.
Sure, there’s a small learning curve for your team at the very beginning. But the enormous leap in security you get far outweighs that tiny adjustment to their workflow. Our focus is always on picking user-friendly methods and providing simple training to make sure the process feels natural from day one.
What Is the Best Type of MFA for a Small Business?
For most small and medium businesses, a quality authenticator app like Google Authenticator or Microsoft Authenticator hits the sweet spot. They offer a great balance of top-notch security, convenience, and low cost. They’re also worlds more secure than SMS codes, which are vulnerable to “SIM swapping” attacks.
Hardware security keys offer the ultimate protection against phishing, but they do have a per-device cost. We usually reserve these for the accounts with the highest privileges—think system administrators or the CEO—or when a business needs to meet specific compliance rules.
You can get a deeper understanding of the different methods by reading our guide on what is two factor authentication and how it strengthens your security.
How Much Does an MFA Rollout Typically Cost?
The cost really depends on your team’s size, how complex your IT setup is, and the MFA methods you choose. The good news is that many of the best solutions, especially those using authenticator apps, are completely free to use.
Where costs can pop up are in a few key areas:
- Professional services for planning the rollout, deploying the tech, and training your staff.
- Subscription fees for more advanced MFA platforms that offer features like conditional access.
- The one-off purchase of hardware keys for your high-risk users.
An experienced IT partner can help you nail down a solution that fits your budget perfectly while still giving you the robust security you need.
What Happens If an Employee Loses Their Phone?
This is a critical question, and it’s something your rollout plan has to address from the very start. A solid process includes having backup verification methods ready to go and a clear, simple procedure for your IT support to reset an employee’s MFA settings.
This often involves pre-generated backup codes that staff can store in a safe, offline place (like a locked drawer or a home safe). Alternatively, an administrator can securely verify the user’s identity through another channel and reset their MFA, ensuring a lost device never locks someone out of their account for long.
How Tbourke Solutions Can Help
This guide gives you the map for rolling out MFA in your business, but you don’t have to navigate that journey alone. At Tbourke Solutions, we partner with Melbourne businesses to deliver MFA deployments that are seamless, effective, and tailored to your unique setup. We take the complexity and guesswork out of the entire process, drawing on over 20 years of hands-on IT experience to make you more secure without getting in the way of productivity.
Our Service Options
We understand that every business has different needs and budgets. That’s why we offer flexible service models.
- Fully Managed MFA Rollout: We handle everything for you. This includes initial planning, risk assessment, technology selection, deployment, user training, and ongoing support. This is the ideal option if you lack in-house IT expertise or want the project completed efficiently with minimal disruption.
- Consultative Approach: If you have an internal IT team, we can act as your expert advisors. We provide strategic oversight, best-practice guidance, and technical backup to ensure your project stays on track and achieves its security goals.
Partnering with us means you get a local team invested in your success. We manage the technical details so you can focus on your business. To get started, visit our contact page and submit a query. We’re here to help you build a stronger, more resilient business.
Share This Story, Choose Your Platform!